

Listen to the article
Britain faces a growing threat of AI-powered cyberattacks capable of disrupting electricity supplies, water systems and food distribution within the next two years, the National Cyber Security Centre (NCSC) has warned.
The agency, part of GCHQ, says hostile states and criminal groups are increasingly able to exploit weaknesses in ageing technology used to operate essential services, raising the prospect of widespread disruption to the British economy.
In its State of the Cyber Nation report published on Tuesday, November 03, the NCSC warns that AI-powered malware is “highly likely” to be used in ransomware attacks against Britain’s critical national infrastructure by 2028.
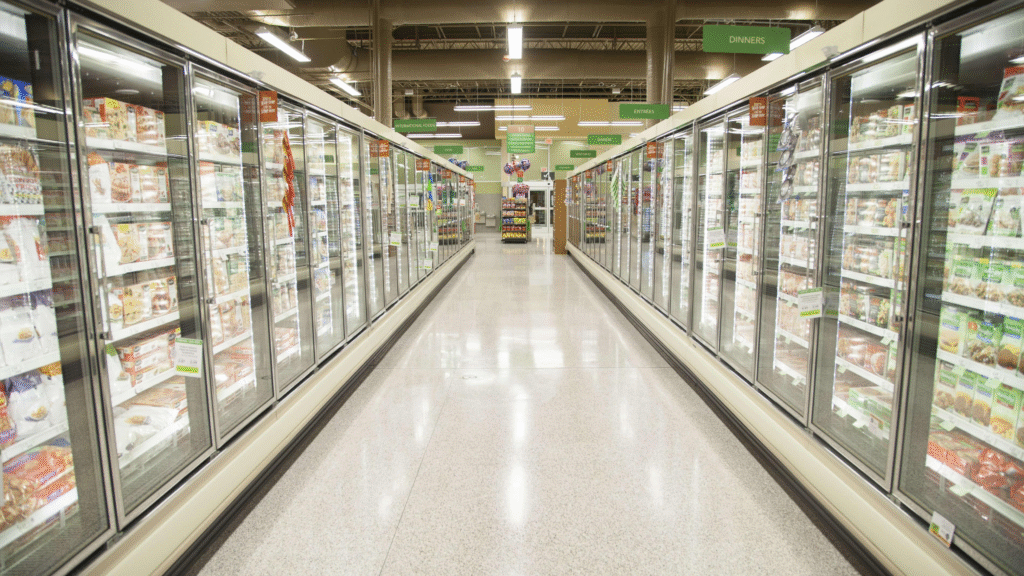
The warning comes as cyberattacks on supermarket refrigeration systems across Europe have exposed how hackers can interfere with equipment controlling physical infrastructure, with some British businesses also affected.
NCSC chief executive Dr Richard Horne said: “In the coming months, we face a real prospect of an unprecedented rise in the number of cyber incidents.”
“But we must be clear that is not because AI has invented new ways to attack us. But because vulnerabilities that have been tolerated for far too long can now be discovered and exploited at a scale that was once unimaginable.”
The NCSC warns that artificial intelligence will increasingly enable hostile actors to automate ransomware operations, identify vulnerable systems and conduct more sophisticated social engineering attacks.
The threat extends to operational technology controlling electricity networks, water facilities, dams, manufacturing systems and refrigeration equipment.
Hackers exploited outdated equipment connected directly to the internet, including systems protected by default passwords, and remotely altered refrigeration temperatures in European supermarkets, causing food to thaw and forcing businesses to discard stock.
The attacks also affected organisations in Britain, where NCSC specialists worked overnight to identify vulnerable systems and contact businesses at risk.
Speaking at the report’s launch, Horne said: “Last night, we had people working through the night contacting organisations that we could see they had vulnerable technology exposed.”
Paul Chichester, the NCSC’s director of operations, confirmed that British businesses had been affected.
“We’re aware of those incidents in the UK, and obviously we’re working with the affected organisations. We’ll keep monitoring that,” he said.
“At the moment, the impact is minimal.”
The refrigeration incidents were not identified as AI-powered attacks. However, they demonstrate how vulnerabilities in physical infrastructure could be exploited more rapidly as attackers adopt artificial intelligence.
The NCSC’s assessment identifies China as the most sophisticated and sustained cyber challenge facing Britain, while Russia continues to conduct operations intended to undermine Western security without crossing the threshold of conventional armed conflict.
Iran-linked groups also remain a concern, with the agency warning that their cyber operations can cause indiscriminate disruption and target individuals considered threats to Tehran.
In July, Horne revealed that approximately three-quarters of cyber incidents affecting critical infrastructure organisations over the preceding year were believed to be linked to state actors.
The agency had managed more than 200 incidents affecting critical infrastructure and its supporting networks in the year to May 2026.
The latest report also highlights the activities of Russian intelligence-linked hackers targeting vulnerable internet routers to gain access to networks associated with critical infrastructure.
In July, the NCSC and international partners issued a joint advisory identifying cyber operations attributed to Russia’s Federal Security Service (FSB), including attempts to exploit weaknesses in network equipment.
The government has announced £60 million for the first phase of a national Cyber Shield, intended to strengthen the country’s ability to detect and defend against malicious activity.
A further £70 million will support a National Exposure and Real-Time Vulnerability Centre, which will use AI to identify weaknesses across critical infrastructure and the wider economy.
A new AI Cyber Security Centre of Excellence in Manchester will also develop specialist expertise within government, while the proposed Cyber Security and Resilience Bill is intended to strengthen security requirements for essential services.
Horne said: “For decades we have collectively got away with tech on the cheap.”
He urged organisations to replace obsolete equipment, restrict unnecessary internet connections and make cyber resilience a fundamental part of their operations.
Horne warned that executives could eventually face having to explain their decisions “when food isn’t on shelves, lights aren’t on, businesses have gone under.”
GCHQ director Anne Keast-Butler said cyber security had become a matter of national defence rather than simply an operational concern for individual organisations.
“We need every organisation in the UK to take action now. Not only to protect their customers, services and livelihoods, but because cybersecurity is now part of the front-line defence of our nation,” she said.
